1024 Resources
Cybersecurity Resources & Blog
Comprehensive resources and AI-powered insights on Governance, Risk, Assurance, Compliance, and Education
Compliance
Learn what to evidence, how to document controls, and what regulators expect when you need to show adequate cyber technological resources.
Oct 05
Compliance
No IT team and cyber feels urgent? Use a risk-based plan aligned to Essential Eight and privacy rules, plus a simple incident prep checklist.
Oct 05
Compliance
Not sure how to prove your information security capability to APRA? See an evidence-led CPS 234/CPS 230 case study and next steps.
Oct 03
Education
Phishing simulation results can mislead. Here’s how to interpret click and report rates, control variables, and turn findings into measurable training.
Oct 02
Education
Security awareness shouldn’t be a checkbox. Build training that measurably changes behaviour using evidence-based, Australia-aligned controls.
Sep 30
Risk
Third-party risk questionnaires get harder—here’s how to answer honestly, with evidence, framework mappings, and practical checks before you submit.
Sep 30
Compliance
A practical case study approach to APRA CPS 234: what to implement, how to prove it, and what to check before your next assessment.
Sep 30
Compliance
Privacy Act reforms may change how you manage data, respond to incidents, and meet privacy obligations. Here’s what to check first.
Sep 30
Compliance
A practical, evidence-based walkthrough for implementing APRA CPS 234—what to do, how to prove it, and where most programs stall.
Sep 30
Compliance
If you’re a financial services business asking “what’s the minimum cyber to stay compliant?”, start with Essential Eight and APRA CPS 234 mapping.
Sep 29
Risk
Supply chain cyber risk isn’t vague—it’s the real ways vendor, software, and partners can affect your systems, data, and obligations.
Sep 29
Assurance
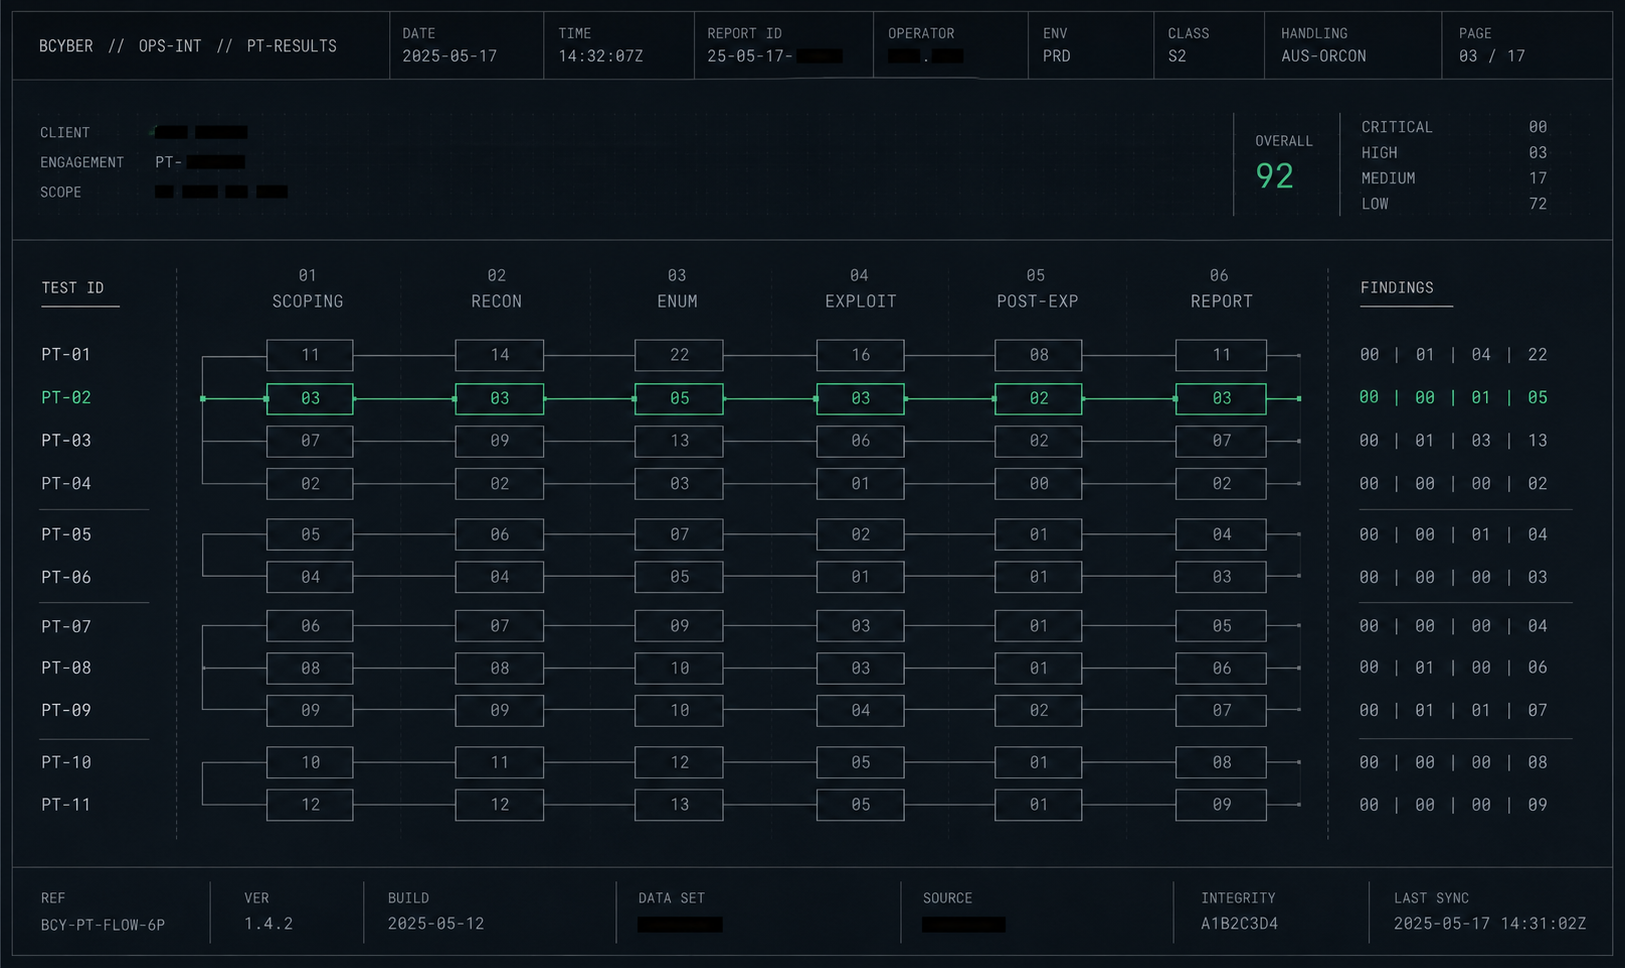
Learn how to convert penetration testing findings into evidence you can defend, remediation you can track, and security improvements you can prove.
Sep 29