1024 Resources
Cybersecurity Resources & Blog
Comprehensive resources and AI-powered insights on Governance, Risk, Assurance, Compliance, and Education
Governance
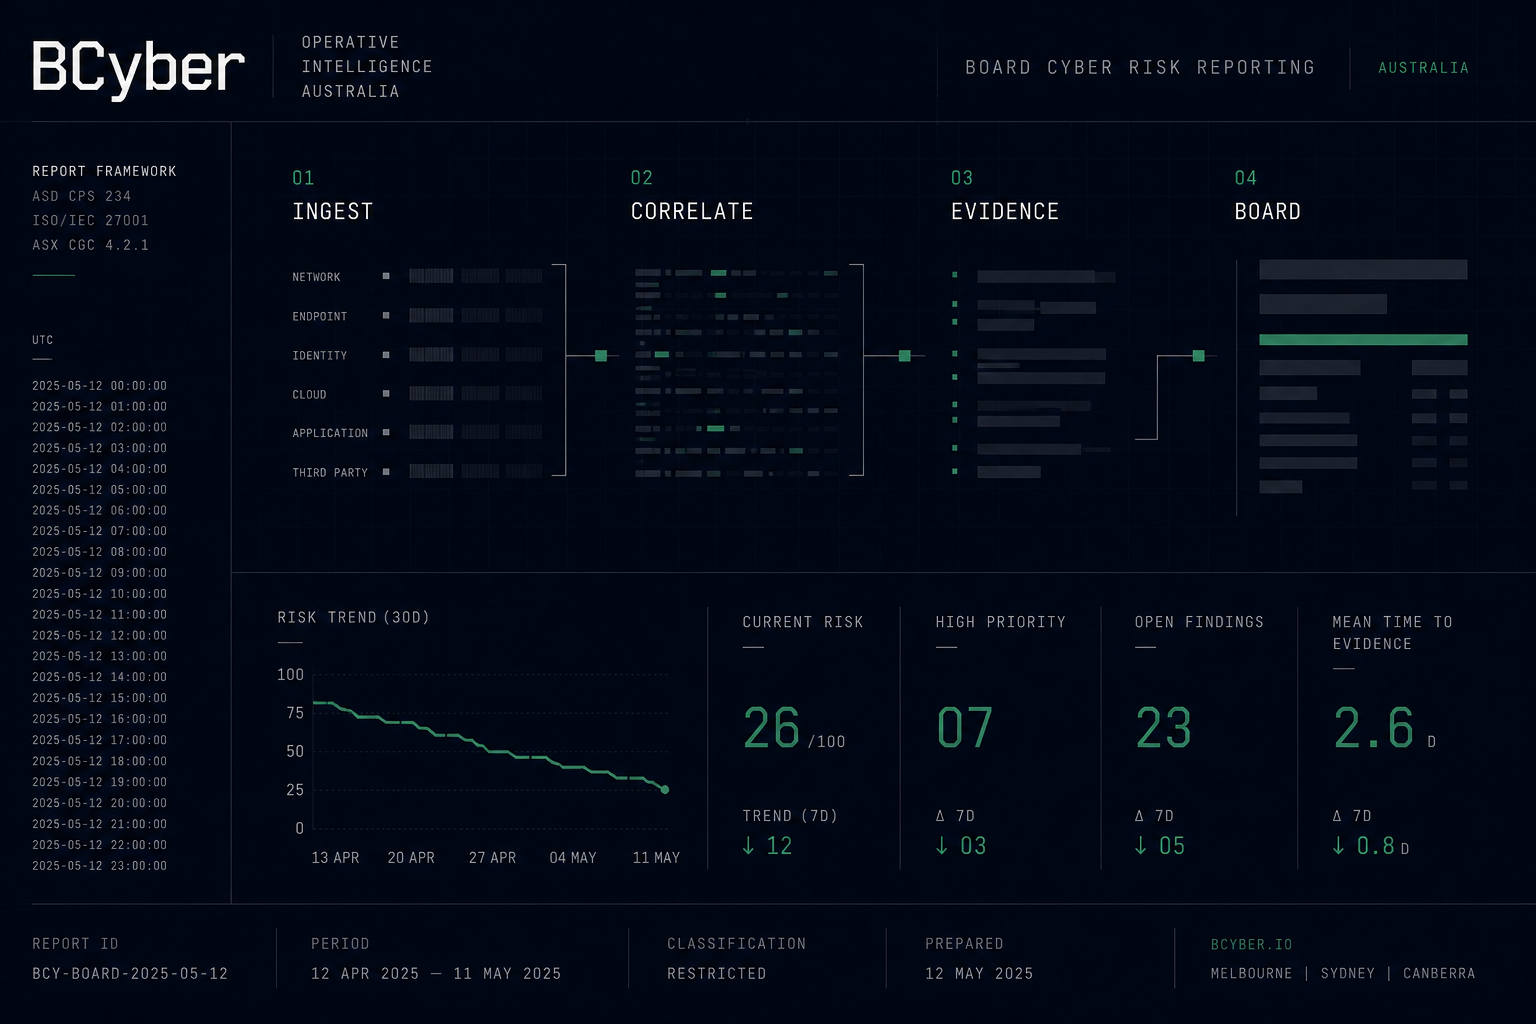
Directors don’t need more cyber chatter—they need decision-ready evidence. Learn what to measure, how to prove it, and next actions.
Oct 08
Compliance
Not sure how much cyber security you need? Use risk and Essential Eight to prioritise what matters most—before the next incident or audit.
Oct 07

Assurance
Don’t file pen test reports away. Learn how to prioritise findings, map evidence to frameworks, and convert results into measurable security improvements.
Oct 07
Compliance
Your customer won’t sign without ISO 27001 or SOC 2. Start with scoping, evidence, and a realistic readiness plan—before you overbuild.
Oct 07
Education
Turn security alerts and reports into board-ready decisions with executive cyber briefings grounded in evidence, priorities, and clear accountability.
Oct 07

Compliance
NIST CSF 2.0 can become a business-ready risk strategy—if you translate functions into decisions, evidence, and continuous improvement.
Oct 06
Compliance
Privacy Act 1988 changes can reshape your obligations. Here’s what to check now—practical steps for governance, security, and privacy risk.
Oct 05
Compliance
A practical AU case study for handling a notifiable data breach under the Privacy Act—how to assess, decide, and notify with evidence.
Oct 05
Compliance
Essential Eight maturity isn’t a scorecard—it’s evidence. See how to assess gaps, improve controls, and demonstrate cyber resilience with ASD-aligned proof.
Oct 05
Compliance
Antivirus and MFA are good starts—but attackers often go around them. Check what else you must prove for Essential Eight and CPS 234.
Oct 05
Compliance
Cyber maturity isn’t a checkbox. Learn how to test whether your controls work in practice—and how to prioritise fixes with evidence.
Oct 05
Compliance
The “cheapest” fix is rarely a tool—it’s the first controls that cut real risk. Here’s how to prioritise the highest-impact steps.
Oct 05