1024 Resources
Cybersecurity Resources & Blog
Comprehensive resources and AI-powered insights on Governance, Risk, Assurance, Compliance, and Education
Compliance
Antivirus and MFA are a start, but professional services threats demand more. Find the gaps in your cyber controls and evidence trail.
Sep 28
Governance
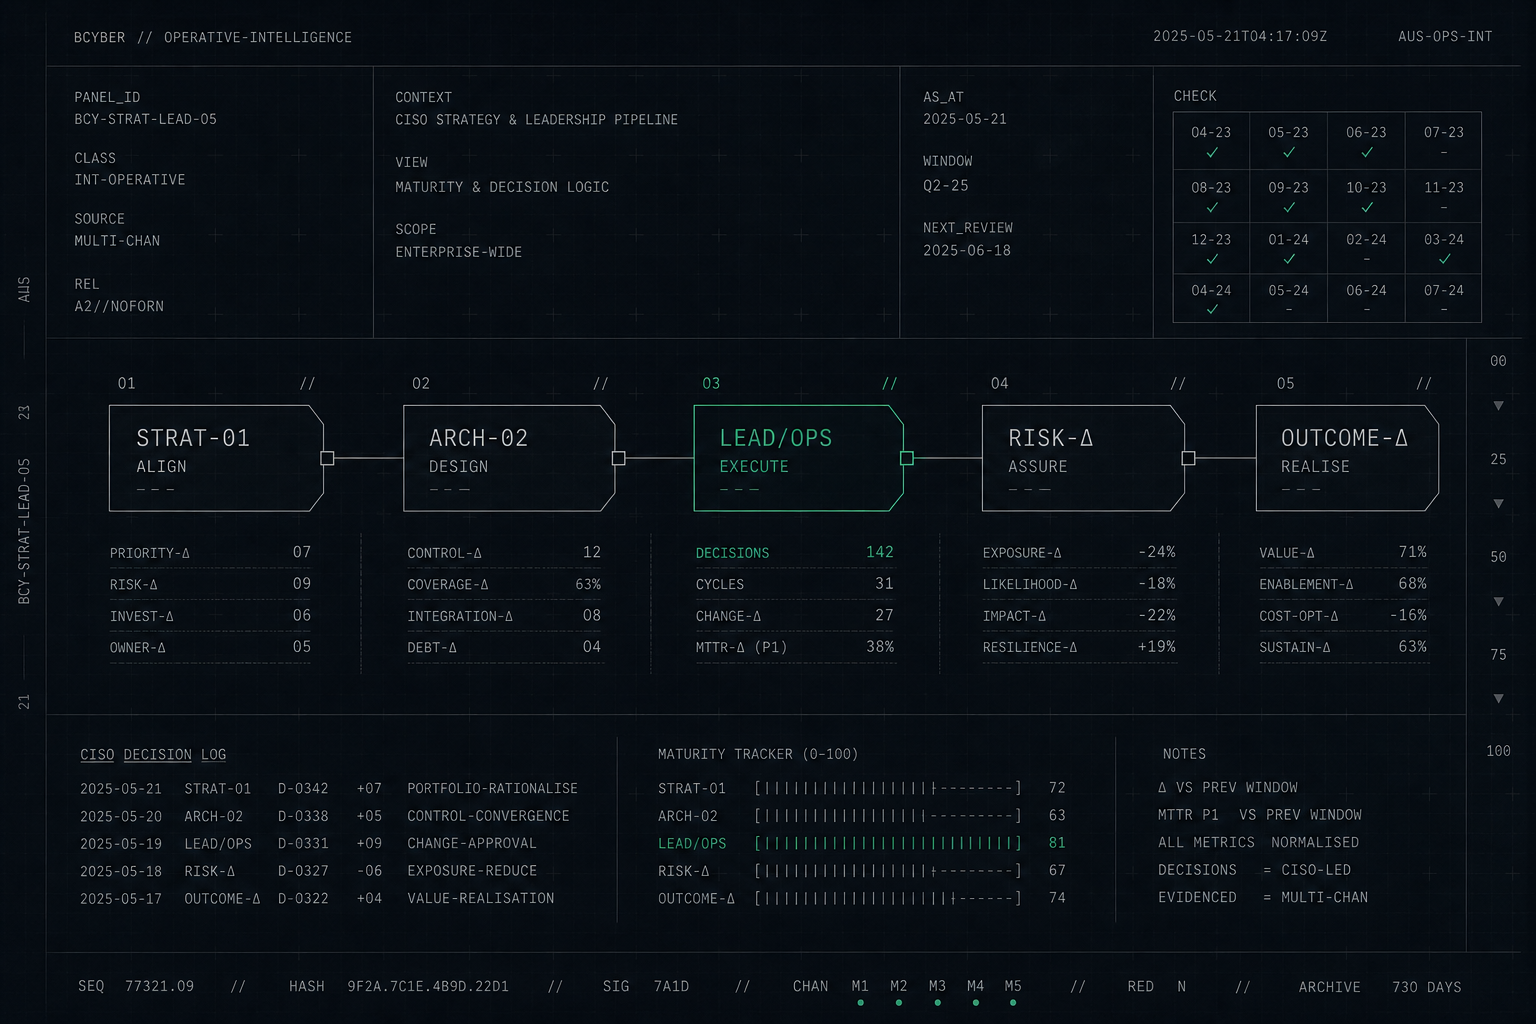
Build a resilient cyber program with CISO strategy, leadership, and proof—mapped to ACSC and Essential Eight, with continuous improvement.
Sep 28
Compliance
If you’re an AFSL and cyber obligations are unclear, this guide maps the key Australian requirements and gives a practical starting plan.
Sep 26
Compliance
Wondering what personal information you’re actually allowed to keep under Australian privacy law? Here’s a practical, evidence-based guide to retention and deletion.
Sep 26
Compliance
Use this practical guide to understand Privacy Act 1988 updates, what the OAIC expects, and how to evidence compliance with the APPs.
Sep 24
Compliance
A client data leak can trigger regulatory action, client churn, and legal risk. Here’s what typically happens—and what to do next in Australia.
Sep 23
Compliance
Unsure what cyber controls an accounting or law firm needs in Australia? Start here with an evidence-based checklist you can act on.
Sep 23
Compliance
Start NIST CSF 2.0 adoption with a governance model, measurable risk reduction, and an implementation plan you can evidence—not guess.
Sep 23
Compliance
Cyber spend feels busy—but does it change risk? Use measurable, evidence-based indicators mapped to Essential Eight, ISO 27001, and APRA CPS 234.
Sep 23
Compliance
A practical, evidence-first guide to measure Essential Eight maturity and prove your cyber resilience—so audits and questionnaires don’t feel like guesswork.
Sep 23
Compliance
Learn a practical way to implement APRA CPS 234: build an evidence trail, prioritise controls, and establish clear accountability for cyber risk.
Sep 23
Governance
Stop drowning in technical alerts. Learn a board-ready way to turn security evidence into clear cyber risk decisions, priorities, and proof.
Sep 23