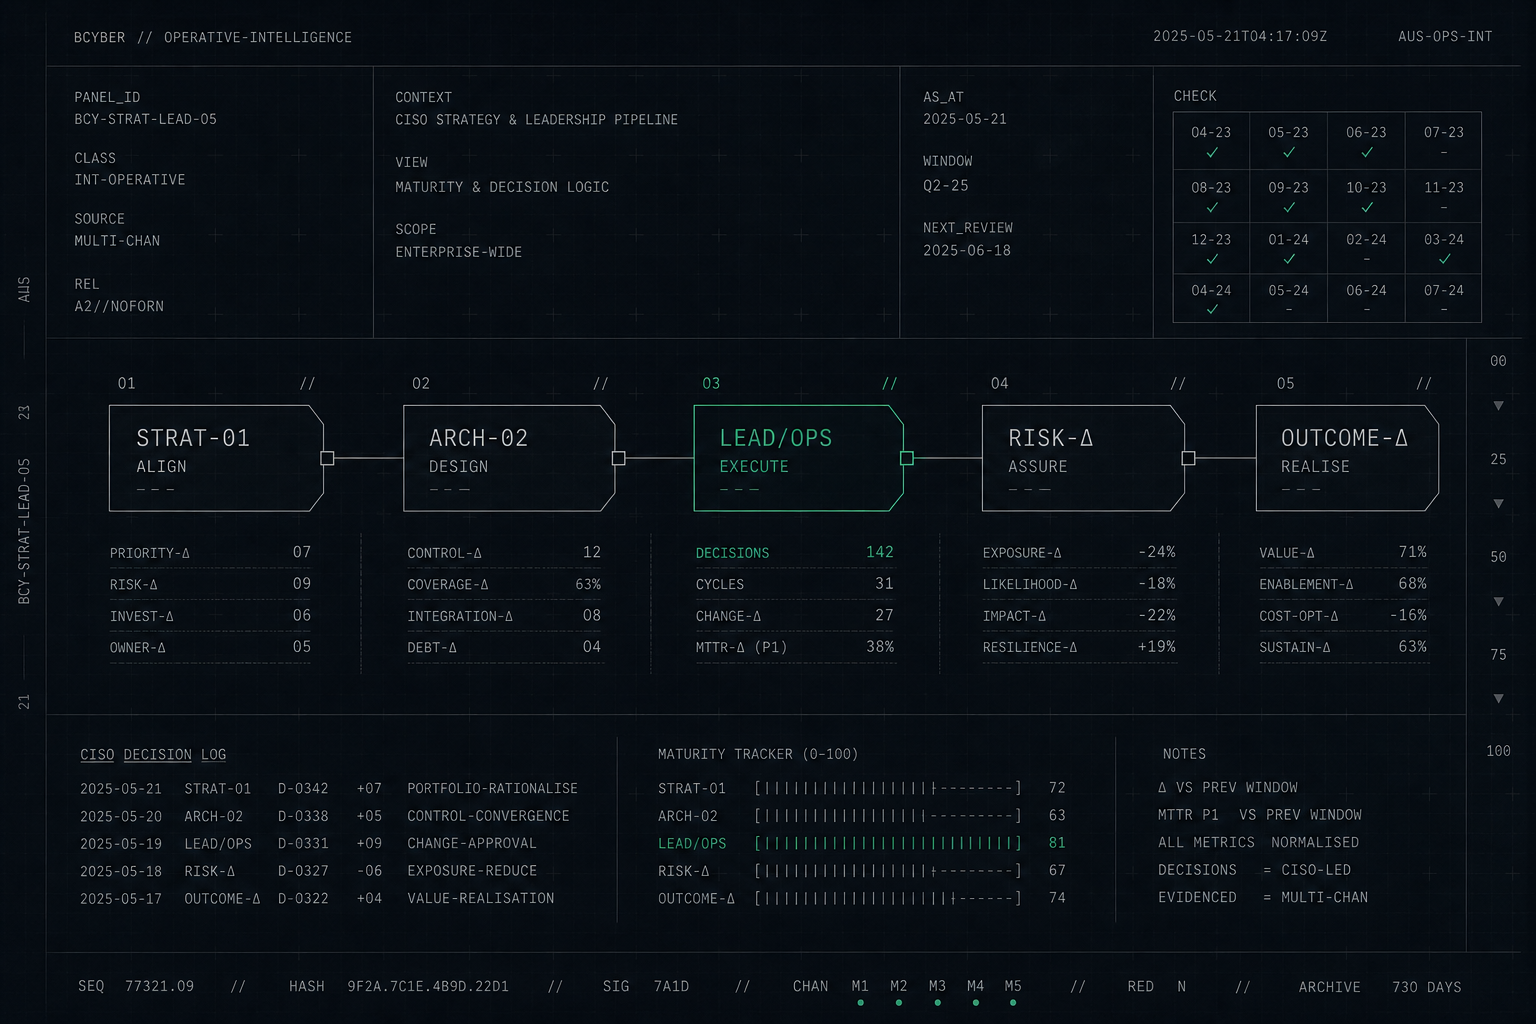
CISO Strategy and Leadership: How to Build a Resilient Cybersecurity Program

By BCyber Security Team | CISSP, CISM Last updated: 28 September 2026
If you are thinking, “I need help fixing our cyber leadership, where do I start?”, start with governance, not tools. CISO strategy and leadership is the discipline of turning cyber from a technical function into a business decision system: clear accountabilities, risk-based prioritisation, evidence, reporting, and improvement. The CISO’s job is not simply to defend systems, but to help the organisation make defensible security decisions and show how those decisions hold up under scrutiny.
In Australia, that means aligning with obligations and expectations from APRA CPS 234, the Privacy Act 1988, the Essential Eight, and sector-specific requirements, while keeping the business moving. For regulated organisations, this often means proving control effectiveness, maintaining timely risk acceptance decisions, and demonstrating that critical assets can be protected and restored under realistic operating conditions.
At BCyber, this governance-first approach is reflected across the GRACE Portal for unified cyber resilience visibility, Paradigm for GRC automation, Profiler for behavioural intelligence, CyberTriage for rapid incident response, Perfect Storm for scenario modelling, and TopSpin for forecasting and capacity planning. These capabilities are designed to support the kind of evidence-based leadership that boards, auditors, and regulators expect.
What does CISO strategy actually mean?
CISO strategy is the way an organisation decides what matters most, what it will protect first, and how it will prove progress over time. It is not a slide deck that sits on a shelf, and it is not a list of tools or controls purchased in response to the last incident. A real strategy sets direction, defines risk appetite, and gives leaders a repeatable way to choose between competing priorities.
In practice, that usually means mapping business services to assets, identifying control dependencies, and setting measurable outcomes such as reduced privileged access exposure, improved recovery time objectives, or lower third-party residual risk. A strong strategy also creates a shared language between executives, technical teams, and the board, so cyber decisions are not made in isolation.
BCyber’s Paradigm platform is aligned to this need through GRC Automation, Risk Quantification, Policy Automation, and Compliance Mapping. That makes it easier to connect strategy to measurable governance outcomes rather than relying on manual spreadsheets and ad hoc reporting.
How strategy differs from operational security work
Operational security is the day-to-day work of patching systems, monitoring alerts, triaging incidents, hardening identity controls, and responding to threats. Strategy sits above that activity and asks whether those efforts are reducing material risk in the right places.
For example, a financial services organisation might have excellent vulnerability management metrics but still be exposed because privileged access review is inconsistent, cloud guardrails are incomplete, or recovery exercises have not been tested against realistic failure modes. In that case, the issue is not lack of activity; it is lack of strategic sequencing. A team can be busy every day and still be misaligned if the work is not tied to business-critical services, regulatory obligations, or known exposure.
What a strong CISO strategy is trying to achieve
A practical CISO strategy usually tries to do five things at once:
- Protect critical assets and services
- Align cyber investment with business risk
- Improve resilience and recovery readiness
- Demonstrate compliance and accountability
- Enable growth without creating unacceptable exposure
Those goals are linked, not separate, because a business cannot treat resilience as an add-on after the fact. If a program cannot explain which risks it is reducing and how that supports operations, it is not yet a strategy. If it cannot be measured, it is likely still a wish.
A useful test is simple: can the CISO explain why a control exists, what risk it reduces, and what evidence shows it is working?
Why strategy must be revisited regularly
Threats change, vendors change, business models change, and regulatory expectations change. A strategy that made sense eighteen months ago may now be misaligned with cloud adoption, remote work, third-party dependencies, or new reporting obligations. That does not mean the strategy was wrong; it means the environment moved.
This is especially relevant for Australian organisations operating under APRA CPS 234, where information security capability must remain commensurate with vulnerabilities and threat posture, and for organisations managing privacy obligations under the Privacy Act 1988, where “reasonable steps” evolve as systems and expectations change. Mature security leadership treats strategy as a living artefact, not a once-a-year exercise.
Why governance comes before tools
Governance is the structure that tells people who decides, who approves, who escalates, and who owns the outcome. Without governance, organisations often buy tools that generate alerts, reports, and dashboards, but no clear action. That is how security teams end up with noise instead of clarity.
At BCyber, this is exactly where the platform ecosystem helps: GRACE Portal provides the single operational view, while Paradigm supports policy and control governance, CyberTriage accelerates incident escalation, and Perfect Storm helps test whether governance assumptions actually hold in a crisis. Governance also prevents the common pattern where every issue becomes urgent and nothing gets solved in a durable way.
How accountability removes ambiguity
Clear accountability is one of the most underrated parts of cyber leadership. The CISO, CIO, risk team, legal, HR, procurement, and business unit leaders all need defined roles, because cybersecurity decisions almost always cross function boundaries.
A simple RACI can help, but only if it is used to support actual decisions rather than filed away for audit season. In a hospital environment, for example, the CISO may own control assurance for clinical systems, but the clinical operations leader may own the business decision to accept downtime risk during a maintenance window. In government, the delegate or branch head may own acceptance of certain residual risks while the security team provides evidence and advice. The important question is not whether someone signed the policy; it is whether the person responsible can act when a risk exception, incident, or third-party issue appears.
What policies, standards, and decision rights should do
Policies should set direction, while standards and procedures make that direction usable. A policy might say access must be controlled, but the standard should define how privileged access is approved, reviewed, and revoked.
BCyber’s real platform content reflects this layered model: the organisation’s 23 policies, 9 processes, 949 published articles, and 539 knowledge hub entries show the value of translating governance into operational guidance. In practical terms, decision rights should be explicit for areas like access exceptions, incident escalation, supplier onboarding, and risk acceptance. If every exception needs executive debate, the process becomes unworkable. If no one can grant or reject an exception, the control environment becomes inconsistent and difficult to defend.
How board and executive oversight should work
Board reporting should not be a technical dump of logs, vulnerabilities, or alert counts. It should be a concise view of business risk, trends, exposure, and progress against agreed priorities.
For APRA-regulated entities, this means reporting in a way that supports CPS 234 evidence requirements and demonstrates that controls are operating effectively. For organisations subject to Australian privacy obligations, reporting should also show whether sensitive data handling, retention, and breach readiness are aligned to the Privacy Act and the Australian Privacy Principles. Executives need to see whether the organisation is strengthening identity controls, improving response capability, reducing third-party exposure, and closing high-priority gaps. In a mature governance model, the board is not asked to manage cyber operations; it is asked to make informed risk decisions.
How do you prioritise cyber risk without getting lost in the noise?
Risk-based prioritisation starts with the uncomfortable truth that not every weakness deserves equal attention. A long vulnerability list can create the illusion of control while the most important systems remain underprotected. The right question is not “What is the most visible issue?” but “What would cause the most harm if it failed, and what is most likely to fail first?”
For example, a financial services firm may have hundreds of low-severity endpoint findings, but the higher-order risk might be a privileged identity path to production systems or weak supplier access governance. A health service may need to prioritise clinical availability, identity assurance, and recovery from ransomware over lower-impact office productivity issues. Strategy becomes practical when it is linked to impact.
How to map risk to business priorities
The first step is to identify the organisation’s critical services, crown-jewel assets, and high-value data. For an AFSL holder, that might include client records, trading or advice systems, identity platforms, or core reporting environments. For a healthcare provider, it may include patient records, clinical scheduling, imaging systems, and connected devices. For a government agency, the priority may be citizen data, service-delivery platforms, and interagency integrations.
Once those assets are visible, the CISO can explain which controls protect them and why those controls matter more than others. NIST CSF 2.0 and ISO/IEC 27001 are useful here because they help connect governance, protect, detect, respond, and recover activities to business outcomes rather than isolated tasks.
Where most organisations should focus first
Some risk areas appear repeatedly because they affect many parts of the enterprise at once:
- Identity and access management: weak identity controls often turn a manageable issue into a serious event
- Cloud and SaaS configuration: misconfiguration can expose data without a dramatic breach
- Data protection and classification: not all information deserves the same treatment
- Third-party exposure: supply chain risk is now part of everyday cyber risk
- Incident response and recovery: resilience is proven when something goes wrong
BCyber’s Profiler supports behavioural analysis, insider threat detection, and access pattern monitoring, which is especially valuable where anomalous logins, privilege misuse, or account takeover risk is a concern. CyberTriage supports 4-minute triage, automated response, and threat containment, which helps reduce dwell time and improve the quality of first response decisions.
How to avoid security theatre
Security theatre is any activity that looks productive but does not materially reduce risk. A busy dashboard, a large number of alerts, or a training completion report may feel reassuring, but they do not automatically translate into better outcomes.
The CISO should use evidence to show which controls are reducing exposure and which are simply creating activity. That often means cutting low-value work so the team can focus on controls that matter. It also means being willing to say “TBD” when the evidence is incomplete, rather than filling gaps with optimism.
If a control cannot be tied to a risk, a service, or a regulatory obligation, it deserves a harder question before more budget is added.
A practical prioritisation sequence
A workable sequence is often easier than a perfect framework:
- Identity
- Critical systems
- Data
- Suppliers
- Response and recovery
That order is not universal, but it is a useful pattern because each step supports the next. Identity reduces lateral movement, critical systems protect business continuity, data controls reduce exposure, supplier controls address external dependencies, and response capability limits the damage when something still gets through.
BCyber’s GRACE Portal is useful here because it provides Cross-product Analytics, Executive Reporting, Compliance Tracking, and Real-time Monitoring in a single dashboard. That helps a CISO see which priorities are moving, which ones are stalled, and where to intervene.
What leadership skills does a modern CISO need?
A modern CISO needs more than technical depth. They need the ability to translate technical issues into business language, build coalitions, and keep people aligned when priorities compete. Security programs fail quietly when the CISO cannot influence the teams that own the systems, the budget, or the business process. That is why leadership is not an optional extra. It is part of the job description, whether the organisation has written it that way or not.
How executive communication changes outcomes
Executives rarely need more technical detail; they need clearer choices. A good CISO brief explains the risk, the business impact, the options available, and the trade-offs between speed, cost, and residual exposure.
For example, in an Australian government environment, a board or executive committee may need to decide whether to accelerate identity hardening now or defer it to protect service continuity during a peak citizen-service period. In healthcare, leaders may need to decide whether to accept temporary downtime risk for patching a clinical application or implement compensating controls and sequence the maintenance differently. That means talking about continuity, legal exposure, operational disruption, reputation, and customer trust, not just vulnerabilities and patches.
How to influence without formal authority
Most CISOs do not directly control the full set of teams needed to secure the organisation. They must work with IT, engineering, procurement, legal, HR, finance, and business unit leaders whose incentives are different from security’s. Influence therefore depends on trust, timing, and relevance.
This is where training and shared understanding matter. BCyber’s platform includes 50 courses with 2 enrollments, and courses aligned to governance and resilience help create the common vocabulary that leaders need. Relevant examples include governance-focused learning paths on GRC, incident response, and privacy obligations. When teams understand why a control exists, they are more likely to support it.
Why culture matters as much as control design
Security culture is the set of habits that shows what an organisation really values. It is visible in how exceptions are handled, how quickly incidents are escalated, and whether people feel safe reporting mistakes.
Training helps, but culture is shaped most strongly by leadership behaviour and process design. If leaders ignore the rules when they are inconvenient, everyone notices. If leaders model accountability and practical caution, the message spreads without needing to be repeated in a hundred policy documents.
What great security teams need from the CISO
Strong teams need role clarity, useful priorities, and space to think. They also need the CISO to protect them from unnecessary noise so they can do the work that matters. A high-performing security function usually includes people with different strengths: analysts, risk specialists, architects, incident leaders, and communicators.
BCyber’s Perfect Storm can support leadership teams with scenario modelling, threat simulation, and resilience testing so the CISO can validate assumptions before a real event. That is especially relevant where the team needs to test compound scenarios such as ransomware plus supplier outage, or credential compromise plus data exfiltration.
How do you prove cyber progress to the board?
Reporting is not administrative overhead; it is one of the main ways a CISO demonstrates value. Good reporting shows where the organisation is exposed, what has improved, what remains unresolved, and what decisions are needed next. If reporting cannot support a decision, it is probably too detailed, too technical, or too disconnected from risk.
What should be reported
The most useful reporting usually covers:
- Current risk posture
- Significant incidents or near misses
- Control coverage and effectiveness
- Compliance gaps
- Remediation progress
- Third-party exposure
- Recovery readiness
For APRA-regulated entities, reports should support evidence of security capability and control effectiveness in line with CPS 234 expectations. For Privacy Act obligations, reporting should support the organisation’s ability to demonstrate reasonable steps, especially where sensitive information is involved. The report should make it easy for leaders to see what needs attention now.
Which metrics actually help
Not all metrics are useful, and some are actively misleading. Raw alert counts can rise or fall for reasons that say little about risk. Training completion rates can be useful, but they do not prove behaviour change.
More meaningful metrics tend to show:
- Control coverage
- Remediation age
- Repeat findings
- Privileged access review completion
- Recovery readiness
- Mean time to contain an incident
- Supplier risk status
- Evidence freshness for audits and attestations
BCyber’s TopSpin supports trend analytics, capacity planning, and performance monitoring, which can help the CISO trend control performance and plan resourcing. The right metric is one that supports action. If a metric does not help the board decide, change, or challenge, it probably does not belong in the pack.
How to make reports business-relevant
Business leaders do not need a translation layer between cyber and business; they need the information framed correctly from the start. A report should explain how a risk affects continuity, revenue, customer trust, operations, or regulatory exposure. It should also show the decision being requested, rather than assuming the audience will infer it.
This is where many programs lose credibility. They report activity instead of insight, and they describe controls instead of consequences. BCyber’s GRACE Portal helps counter that by consolidating cross-product data into executive reporting that is easier to read and harder to misinterpret.
What a good review cadence looks like
A useful cadence often includes monthly operational reviews, quarterly executive reviews, and board-level risk updates on a regular schedule. High-priority remediation items should be tracked continuously, not only when a meeting is approaching. That cadence helps security become part of the management rhythm rather than an exception to it. It also creates a visible evidence trail for audits and assurance work.
How does a CISO drive continuous improvement instead of one-off fixes?
A mature cyber program improves because it learns. Incidents, audits, assessments, and near misses should all feed back into strategy, governance, and control design. If the same finding keeps reappearing, the issue is no longer only technical; it is structural.
BCyber’s platform data reflects the importance of this learning loop: 14 fact-find assessments and a large body of operational content in the knowledge hub indicate that improvement is driven by evidence, not intuition. Continuous improvement means the organisation is changing the way it works, not just patching the latest gap. That is what turns cybersecurity from a project into a capability.
How to assess maturity without becoming framework-driven
Frameworks such as ISO 27001, the Essential Eight, and NIST CSF 2.0 are useful because they provide structure and comparability. But the framework should serve the business, not replace judgement. A maturity assessment is most valuable when it shows which areas are stable, which are brittle, and which need investment first.
That assessment should look across people, process, and technology together, because weaknesses often appear at the boundaries between them. A program can score well in theory and still fail in practice if adoption is poor. BCyber’s Paradigm supports policy automation and compliance mapping, which can help keep the maturity model connected to actual controls and evidence.
How incidents and audits should feed the roadmap
Every incident and audit finding is a chance to sharpen the roadmap. If an incident exposed gaps in logging, escalation, or recovery, the response should not stop at closing the ticket. It should trigger a review of control design, ownership, training, and governance. The same is true for audit findings.
For example, if a healthcare provider experiences delayed incident escalation because clinical and IT teams used different reporting paths, the fix is not only a process note. It may require role updates, on-call changes, training, and automation in the incident workflow. BCyber’s CyberTriage can help standardise the initial triage path and improve containment discipline.
What a credible roadmap looks like
A good roadmap is tied to risk reduction, not just compliance deadlines. It should sequence work according to dependencies and business impact, and it should show why one item is ahead of another. For example, improving identity controls may come before a broader cloud uplift because the former reduces exposure across many systems at once. The roadmap should also show who owns each action and how progress will be tracked. If the roadmap changes, the reason should be visible, not hidden.
How to show progress over time
Progress should be visible in exposure reduction, better recovery performance, fewer repeat findings, and stronger decision discipline. The point is not to grow the program endlessly; it is to reduce material risk and improve confidence in how the organisation responds.
A cyber program that gets larger but not clearer is not necessarily maturing. A program that becomes more disciplined, more measurable, and more predictable is on the right path. That is the kind of improvement leaders can explain to the board and prove to auditors.
How BCyber’s platform supports CISO governance and leadership
BCyber’s CyberSuite is designed to support governance-led cyber leadership across the full lifecycle:
- GRACE Portal: unified cyber resilience visibility and executive control
- Paradigm: AI-self-learning GRC automation and policy management
- Profiler: behavioural intelligence for insider risk and access anomalies
- CyberTriage: AI-powered incident response with rapid triage
- Perfect Storm: scenario intelligence and resilience testing
- TopSpin: forecasting and trend analysis for capacity and risk planning
- Privacy in Depth: privacy management for Australian privacy obligations
This ecosystem is relevant to organisations operating under APRA CPS 234, the Essential Eight, NIST CSF 2.0, and ISO 27001, especially where evidence, repeatability, and board reporting matter. BCyber has also been recognised as:
- 2025 Finalist Cybersecurity Professional Of The Year — Karen Stephens, Co-Founder & CEO
- 2025 GRC Provider of the Year — Finalist
- 2025 AI Innovator - Cyber Security — Finalist
Key takeaways
CISO strategy and leadership are about making cybersecurity a structured decision capability, not just a technical service. Governance should come first, because clear accountabilities and decision rights make every other control more effective. Risk-based prioritisation keeps the team focused on business-critical exposure instead of the loudest problem of the week. Executive communication, board reporting, and continuous improvement are what turn good intentions into an evidence-based program.
The strongest CISO programs ask hard, useful questions: what matters most, who owns the decision, what evidence supports it, and what changes next. That is how cyber becomes part of enterprise leadership rather than a separate, reactive function. In the Australian context, the answer should always be anchored to real obligations, practical controls, and visible proof.
If your current program cannot explain those things clearly, it may be time to revisit the governance model before adding anything else.
Sources and verification
Verification statement: Platform statistics referenced in this article are based on BCyber real platform data provided for editorial use, including policies, processes, courses, articles, knowledge hub entries, clients, and fact-find assessments. Regulatory and framework references below are linked to authoritative public sources.
Authoritative references
- APRA CPS 234 Information Security: https://www.apra.gov.au/information-security
- Australian Signals Directorate (ASD) Essential Eight: https://www.cyber.gov.au/resources-business-and-government/essential-cyber-security/essential-eight
- Australian Cyber Security Centre (ACSC): https://www.cyber.gov.au/
- NIST Cybersecurity Framework 2.0: https://www.nist.gov/cyberframework
- NIST SP 800-53: https://csrc.nist.gov/publications/detail/sp/800-53/rev-5/final
- ISO/IEC 27001 overview: https://www.iso.org/isoiec-27001-information-security.html
- Office of the Australian Information Commissioner (OAIC) Privacy Act resources: https://www.oaic.gov.au/privacy/privacy-legislation/the-privacy-act
- Australian Signals Directorate, Incident response guidance: https://www.cyber.gov.au/resources-business-and-government/essential-cyber-security/incident-response


